ANTIPODES SECURITY
Enterprise-Grade Cyber Leadership. Without the Full-Time Cost.
Build board-ready governance, pass enterprise scrutiny, and align security with growth—guided by a Chief Cyber Strategist and 20+ year CISSP with leadership experience across Cigna, Diageo, GE, and Gartner.
Antipodes Security
Areas of Expertise
Broad cybersecurity expertise—spanning board governance, security architecture, and cross-border regulatory alignment—tailored to your organization's risk profile.
Antipodes Security delivers targeted advisory and architectural guidance across these core disciplines:
Antipodes Security also advises on specialized risk assessments and custom engagements beyond these core disciplines - contact the firm to discuss your scope.
Antipodes Security
Mark Hart, CISSP - Principal & Founder
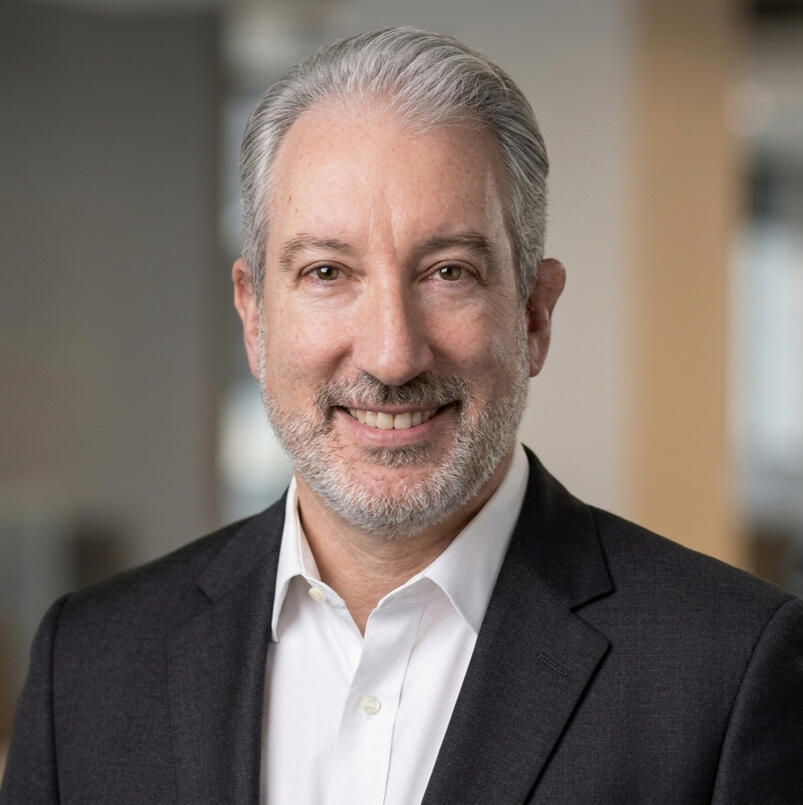
Mark Hart brings 30+ years of experience across enterprise technology, IT, and cybersecurity—including over two decades as a CISSP—spanning senior leadership and architecture roles at Cigna, Diageo, GE, and Gartner.Alongside that enterprise foundation, he has built and advised high-growth startups via hands-on commercial business development and CISO leadership—pairing enterprise governance rigor with startup agility and customer awareness— enabling the delivery of board-ready strategy, customer assurance, and pragmatic security architecture tailored to your stage.
Antipodes Security
Schedule a Confidential Conversation
Connect directly via the form or calendar below to discuss your organization's risk profile and explore how an independent executive cyber advisory service may support your leadership team.
Or select a time below for a confidential conversation.
Frequently Asked Questions
What industries does Antipodes Security serve?
Antipodes Security provides executive cybersecurity advisory services across complex sectors—specializing in protecting critical data and intellectual property for organizations in healthcare, defense, financial services, industrials, advanced research, and consumer products.
Which regulatory and cybersecurity frameworks do you support?
The practice provides strategic architecture design, governance alignment, and readiness across major commercial and regulatory frameworks—spanning global standards (NIST CSF, ISO 27001, SOC 2), U.S. regulated sectors (CMMC, HITECH), and EU/UK regimes (GDPR, DORA, Cyber Essentials).
How does an independent cybersecurity advisory engagement work for cross-border compliance?
Delivered from the United States, Antipodes Security serves as a dedicated, independent advisor to your leadership team—providing direct, board-ready cyber guidance while your leadership retains full operational and risk-acceptance authority. Whether supporting U.S.-based organizations expanding internationally or foreign-headquartered firms navigating U.S. and global expectations, The practice assesses your current security posture, maps controls against target domestic and international frameworks, prioritizes remediation roadmaps for your internal or technical teams, and delivers ongoing strategic guidance to keep your business audit-ready across jurisdictions. (Hands-on technical implementation or remediation is excluded from standard advisory engagements and available only under a separate Statement of Work.)
Do you provide technical cyber architecture design alongside executive strategy?
Yes. Antipodes Security consulting services bridge the gap between high-level executive advisory services and technical security design—specializing in defensive cyber reference architectures (AWS/Azure), including zero-trust cloud design blueprints, operational technology (OT) segmentation strategies, and secure system mapping for defense contractors. The practice ensures your actual technical infrastructure matches your strict compliance mandates.
How does Antipodes Security deliver an enterprise-level compliance and security roadmap?
Antipodes Security operates as a principal-led advisory practice—eliminating big-firm overhead and junior-analyst handoffs so your leadership team works directly with a seasoned cyber executive and chief architect. Drawing on over two decades of CISSP-certified leadership—including executive presence in the boardroom, deep technical architecture expertise, and experience leading complex engineering organizations—Antipodes Security designs your overarching security strategy, governance structure, and multi-framework compliance roadmap. From there, the practice guides and collaborates closely with your in-house IT, engineering teams, or MSPs as they execute the technical implementation—giving you Fortune 500-caliber direction without full-time executive overhead.
Privacy Policy
Last Updated: November 2026
This Privacy Policy outlines how Antipodes Security LLC ("Antipodes," "we," or "us") collects, uses, and safeguards information when you visit this website or submit data through our intake forms. As a specialized cybersecurity consulting firm, data protection and confidentiality are our highest operational priorities.
1. Information We Collect
We collect information that you voluntarily provide to us when requesting a consultation, scheduling a consultation via Cal.com, or contacting us directly. This information may include your name, corporate email address, phone number, company name, target industry, and specific compliance framework requirements (such as NIST, CMMC, HIPAA, or GDPR). Our website host and scheduling provider may also automatically collect technical information, such as your IP address, browser type, and pages visited, and may set cookies needed to operate their services. We do not sell your personal information or use it for targeted advertising. This website does not respond to browser "Do Not Track" signals.
2. How We Use Your Data
Any information you submit is used strictly to evaluate your operational security requirements, prepare for an initial consultation, and deliver our cybersecurity advisory and architecture guidance services. We share your information only with service providers that host this website, schedule meetings, and deliver email for us, and only as needed for those functions. We may also disclose information when required by law or legal process.
3. Confidentiality & Security Protocols
We treat submitted inquiries as confidential and use reasonable administrative, technical, and physical safeguards designed to protect them. This website uses HTTPS encryption in transit. No method of transmission or storage is completely secure, and we cannot guarantee the security of information you send to us. For clients in defense, healthcare, or financial sectors, formal Non-Disclosure Agreements (NDAs) can be executed prior to discussing specific infrastructure details or regulatory audit findings. Please do not submit protected health information, passwords, system credentials, or details of specific vulnerabilities through this website or its scheduling tool.
4. Your Privacy Choices
You may ask us to access, correct, or delete personal information you submitted through this website. To make a request or submit a security disclosure, email [email protected]. We will respond within forty-five (45) days.
5. Data Retention
We keep inquiry and scheduling information only as long as needed to respond to you, evaluate a potential engagement, and meet legal and recordkeeping obligations, and no longer than 12 months after our last contact with you unless you become a client. Information about clients is retained as stated in the applicable Master Services Agreement.
6. Children's Privacy
This website is intended for business users and is not directed to children under 13. We do not knowingly collect personal information from children under 13 and will delete any such information we learn we have received.
7. Changes to This Policy
We may update this Policy by posting a revised version with a new "Last Updated" date. Before a material change applies to personal information you already provided, we will notify you through the contact information you gave us.
Terms of Service
Last Updated: November 2026
Welcome to our website. By accessing this site, you agree to comply with and be bound by the following terms and conditions of use. If you disagree with any part of these terms, please do not use our website or request advisory services through our portal.
1. Nature of Services
This website provides information regarding independent cybersecurity advisory and architecture guidance services offered by Antipodes Security LLC, a Connecticut limited liability company ("Antipodes," "we," or "us"). The information, insights, and framework overviews presented on this website are for general educational and strategic guidance purposes only. Nothing on this website constitutes legal advice, professional advice about your specific systems or environment, or a guarantee of any security, audit, or regulatory compliance outcome. You should not act on website content without advice tailored to your organization.
2. No Professional-Client Relationship
Accessing this website, submitting an inquiry through our contact forms, or scheduling an introductory consultation via Cal.com does not establish a formal consulting or fiduciary relationship. A professional advisory relationship is established only when Antipodes and the client sign a written Master Services Agreement (MSA) and a Statement of Work (SOW) issued under it.
3. Intellectual Property
All original content, text architecture, service frameworks, and structural methodologies displayed on this website are the intellectual property of our LLC. Unauthorized reproduction, distribution, or commercial exploitation of this material without prior written consent is strictly prohibited.
4. Limitation of Liability
Cybersecurity frameworks and standards, such as NIST publications and CMMC, and laws and regulations, such as HIPAA and GDPR, change frequently, and website content may not reflect the latest version. We assume no liability or responsibility for errors or omissions in the content of this site, or for any operational, financial, or regulatory impacts resulting from your use of the general information provided here. This website and its content are provided "as is," without warranties of any kind. To the fullest extent permitted by law, our total liability arising from your use of this website will not exceed one hundred dollars ($100), and your sole remedy for dissatisfaction with the website is to stop using it.
5. Governing Law
These Terms are governed by the laws of the State of Connecticut, without regard to its conflict-of-laws rules. Any dispute arising from your use of this website will be resolved exclusively in the state or federal courts located in Connecticut, and you consent to their jurisdiction.
Security & Trust Posture
Last Updated: November 2026
Antipodes Security LLC applies defense-in-depth practices across its digital presence and client communications.
1. Website & Infrastructure Security
Transport Encryption: All traffic to this website is encrypted in transit using TLS 1.2/1.3 with HTTP Strict Transport Security (HSTS) enforced.
Edge Protection & Security Headers: Public web traffic is routed through Cloudflare edge infrastructure with hardened HTTP response headers (Content-Security-Policy, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, and Permissions-Policy) and automated bot and DDoS mitigation.
Minimal Attack Surface: This site operates as a static architectural front end with no local customer database, user login portal, or stored client documents on the web server.
2. Secure Engagement & Data Handling
Intake Hygiene: Do not submit sensitive architectural diagrams, credentials, system vulnerabilities, or regulated data (such as PHI or CUI) through the public website contact form or scheduling tool.
Confidential Channels: Prior to sharing sensitive technical or audit materials, Antipodes Security executes a mutual Non-Disclosure Agreement (NDA) and establishes encrypted document-exchange channels appropriate to the engagement's classification requirements.
3. Vulnerability Disclosure
Antipodes Security welcomes good-faith security reports regarding our public web properties or email domain. If you identify a potential vulnerability or misconfiguration, please report it to [email protected] with sufficient detail to reproduce the issue. Please do not conduct disruptive testing, automated scanning, or data exfiltration against shared hosting infrastructure.